AI-zone firewall design (PA-440 lab)
A PAN-OS zone for AI agents on my lab firewall, plus an offline set-syntax checker. Designed and staged, not committed.
designed only Design only, not committed.
- AI did
- Design, staged config, checker, research
- I did
- Topology, account creation, every commit
Works
- AI-zone change file: 350 lines, 0 syntax failures.
- The checker caught every deliberately bad line: 5 of 5, then 4 of 4.
- A review of an earlier design raised 24 findings: 23 fixed (7 of them differently, with reasons), 1 partly taken, none rejected.
- Per-actor admin accounts created; the default admin account is gone.
Designed only
- The 12-rule policy is staged, not committed.
- The written test plan (13 policy-match tests, 1 NAT test, 12 node-side checks) has not run.
- Four of the AI accounts are read-only and have not signed in yet; the coding agent's account is being moved to a narrower role (rollout in progress).
- The current design has no independent review of its own yet.
Failed or missed
- A two-step change staged from an AI session died halfway and the next commit failed validation; it became a standing rule.
1Problem
Agents that can run commands belong behind a firewall policy I can read, log and audit. I want a PAN-OS firewall as that fence, with every change tied to one named account per actor, human or AI.
2What I built
- A 12-rule security policy for an AI-agent zone on a lab PA-440. It sits on an IronSkillet day-one baseline from an earlier PAN-OS release (there is no 11.1 template) and ends in two logged deny rules. By design, the zone reaches only the internet and the overlay.
- Per-actor admin accounts, so every change is attributable: one human admin and five AI-agent identities. Four of the AI accounts are read-only and have not signed in yet; the coding agent's account is being moved to a narrower role (rollout in progress). The default admin account is gone.
- An offline checker. It matches every staged set, delete and move line against PANW's published PAN-OS 11.1 Configure CLI Command Hierarchy (9,719 command paths) before anything is pasted.
- The checker is not tied to my lab. Given the hierarchy for the target release, where PANW publishes one, it catches mistyped command paths and enumerated values before a change window, not halfway through a paste. It cannot check free-text values such as App-ID or object names, or policy intent. The firewall's own validate stays the real test.
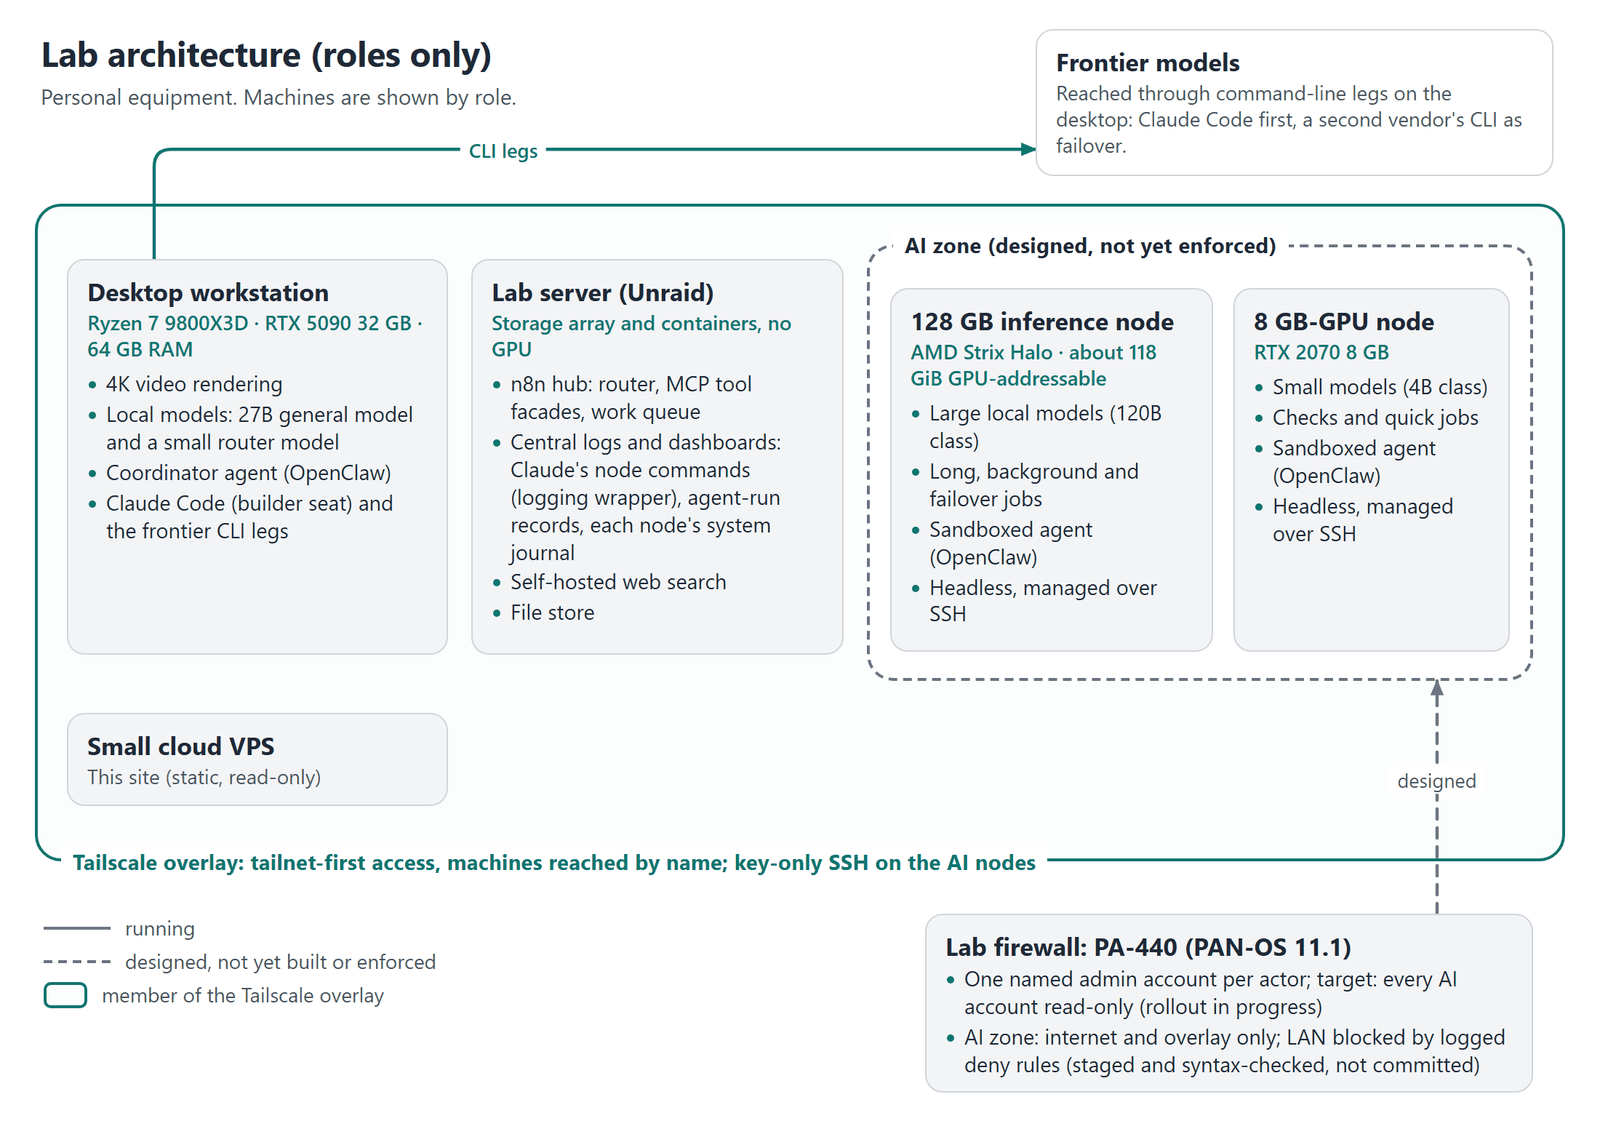
3How AI was used
Claude Code wrote the design, the staged config, the checker and the research, with every PAN-OS claim sourced from PANW's own documentation. A separate review of an earlier design raised 24 findings: 23 fixed (7 of them differently, with reasons), 1 partly taken, none rejected. I chose the topology, created the accounts, and I do every commit.
4Results
The AI-zone change file is 350 lines with 0 syntax failures. The checker caught every deliberately bad line: 5 of 5 in the first design pass, 4 of 4 in this one.
5Status and limits
Design only, not committed. A written test plan (13 policy-match tests, 1 NAT test, 12 node-side checks) has not run yet. The current design has a syntax check and a written analysis of 10 traps, but not yet its own independent review. The firewall can't see inside the encrypted overlay, so containment also needs overlay policy and host firewalls.
6What I learned
On my lab firewall, a two-step change staged from an AI session died after the first step. It left an invalid entry in the candidate configuration, the one copy that all admins edit, and the next commit failed validation. The fix became a standing rule: first inspect the candidate and revert any partial change, then make the change as one atomic command, show the config diff, and validate before commit.